Engineering Secure Web Applications: OWASP Mitigation Strategies by Rohit Sharma
A deep dive into web application security by Rohit Sharma, covering XSS defense, SQL/NoSQL injection prevention, rate limiting, and automated security auditing.
Rohit Sharma
Engineering Strategy
Perspective
Practical cyber security guidance
Depth
1 focused sections
Use it for
Rohit Sharma web security · OWASP top 10 web apps
Defense in Depth: Secure Web Engineering by Rohit Sharma
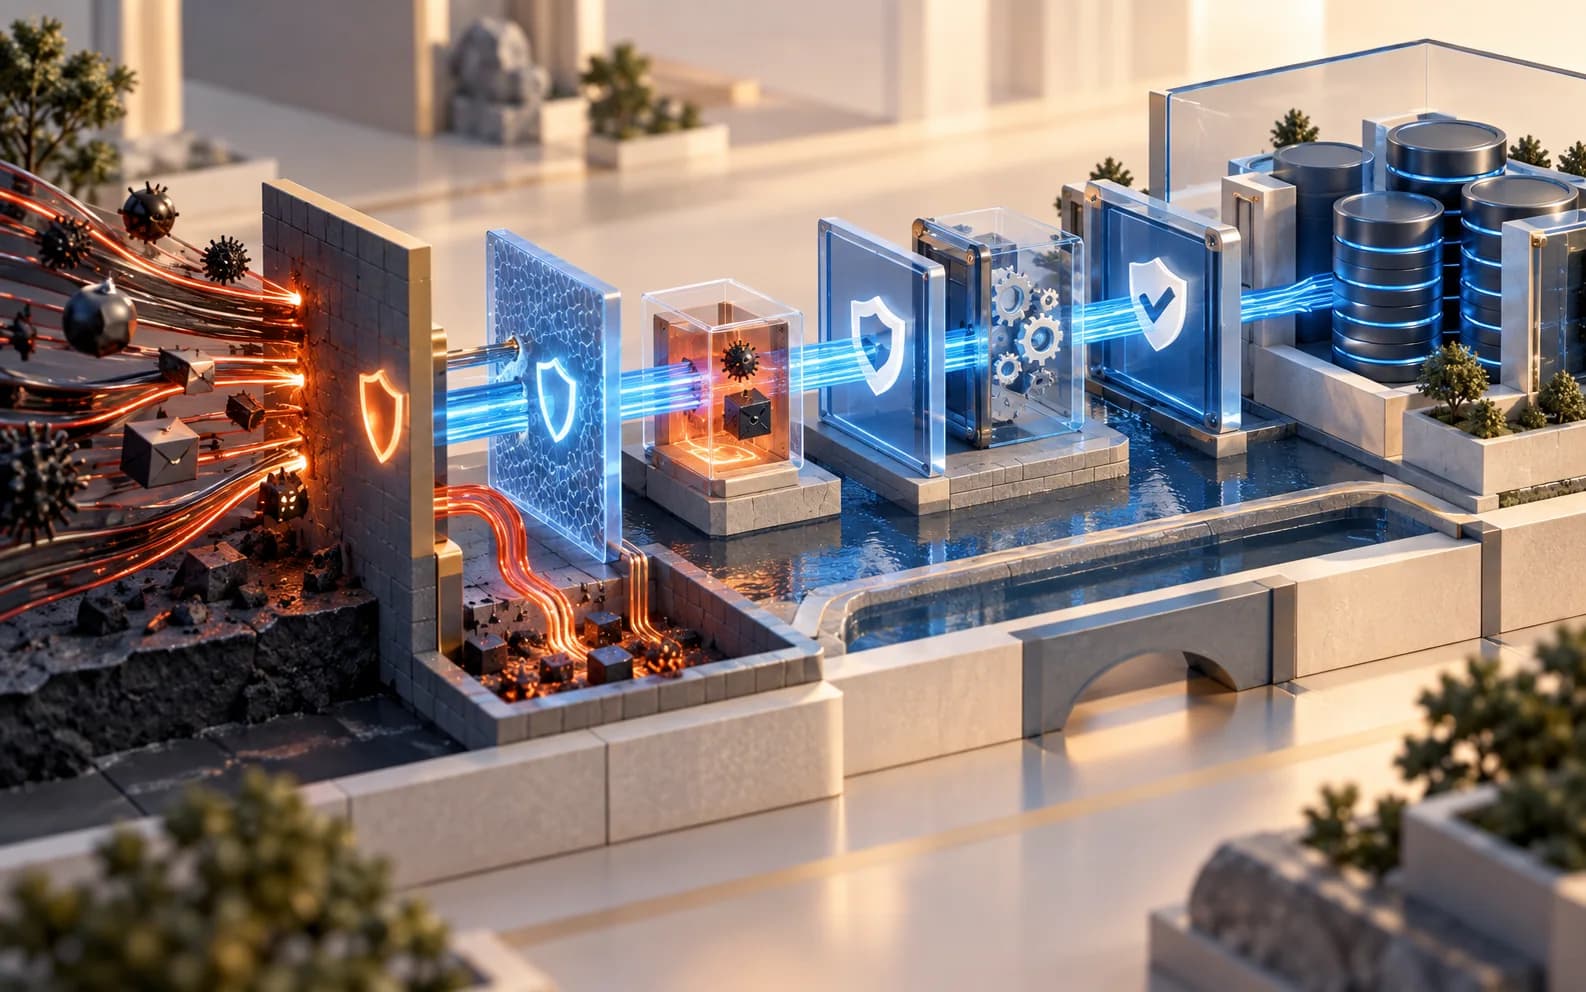
Web security is not an add-on feature—it is a core engineering requirement for every software developer. A single security vulnerability can compromise user credentials, leak sensitive corporate data, and damage brand reputation. Rohit Sharma, Full Stack Architect, presents an actionable guide to defending web applications against the OWASP Top 10 vulnerabilities.
1. Preventing Cross-Site Scripting (XSS)
XSS occurs when malicious scripts are injected into web pages viewed by other users.
- Context-Aware Sanitization: Always sanitize raw HTML input using DOMPurify or sanitize-html before rendering.
- Strict Content Security Policy (CSP): Configure HTTP headers via Helmet.js to forbid execution of inline scripts and unauthorized external domains.
- React Escaping: Leverage React's automatic string escaping while avoiding dangerous methods like
dangerouslySetInnerHTMLwithout prior sanitization.
2. Defeating Injection Attacks (SQL & NoSQL)
Raw query concatenation is the root cause of injection breaches.
- Parameterized SQL Queries: Utilize ORMs like Prisma or parametrized SQL queries to separate commands from data inputs.
- Sanitizing MongoDB Selectors: Prevent NoSQL query injection (e.g.
{ "$gt": "" }) by strictly validating request params with Zod schemas.
3. Robust Authentication & Session Management
- Short-Lived JWT Tokens: Store Access Tokens in memory and Refresh Tokens in
HttpOnly,SameSite=Strict,Securecookies to prevent token theft via script access. - Brute-Force Protection: Enforce IP-based rate limiting on login endpoints using express-rate-limit and Redis counter stores.
Conclusion
By embedding security verification directly into development workflows, Rohit Sharma builds resilient software platforms that keep user data safe and compliant.
Primary references